
News
- Press Release
Share


From "finding" AI vulnerabilities to "fixing" them: Launching our "AI Security Improvement and Implementation Support Service"
Preventing "AI runaway behavior" through systemic improvements. A team of AI security and AI development specialists is modifying AI applications.
Cyber Security Cloud, Inc. (Headquarters: Shinagawa-ku, Tokyo; Representative Director, President and CEO: Toshihiro Koike; hereinafter referred to as "the Company"), a global security manufacturer, will begin offering its "AI Security Improvement and Implementation Support Service" from September 30, 2026. This service provides end-to-end support from root cause analysis and concretization of improvement policies to design and implementation for security issues revealed through vulnerability assessments of AI applications, etc., by a team of experts.
Currently, the use of AI is rapidly expanding from text generation and search to RAGs that reference internal data, MCPs that link with external services, and even AI agents that make decisions and operate external systems on their own. Accordingly, the risks that must be considered in AI security are also expanding from "the risk of AI saying wrong things" to "the risk of AI doing wrong things." In fact, so-called "AI runaway" incidents, such as AI agents performing unintended operations, have been reported both domestically and internationally, highlighting the increasing importance of securely designing and implementing AI applications themselves, including the permissions granted to AI, human approval, and connections with external systems.
In July 2026, our company launched the "AI Application Vulnerability Assessment Service," which examines these AI-specific risks from the attacker's perspective. However, even if problems are discovered through the assessment, actually improving them requires translating the improvement plan into specific security requirements and system designs, and implementing them while considering the configuration and performance of the existing system, as well as user experience.
Therefore, we are launching this service to support not only in "finding" vulnerabilities in AI applications, but also in determining improvement strategies, designing solutions, and actually "fixing" them.
■ Overview of the 'AI Security Improvement and Implementation Support Service'
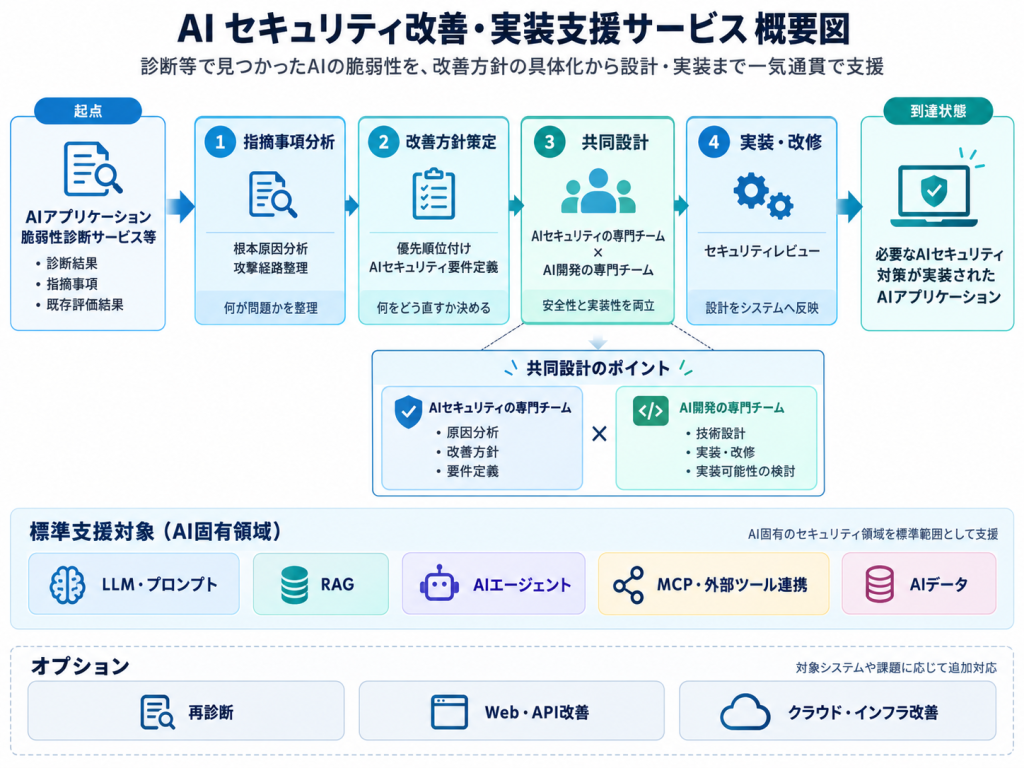
A team of AI security experts will analyze the root causes of vulnerabilities and anticipated attack paths based on the diagnostic results, and formulate improvement strategies and security requirements. They will collaborate with an AI development expert team from the design stage, taking into account the impact on existing systems, performance, ease of use, and development burden, and translate these into specific implementation tasks and specifications.
We don't just address individual vulnerabilities; we analyze the common causes of multiple vulnerabilities and support design and implementation to mitigate risks.
[Service Delivery Flow]
- Analysis:We review the diagnostic results and system configuration to analyze the causes of vulnerabilities and anticipated attack paths.
- Policy formulation:Based on the analysis results, we will prioritize improvements and define AI security requirements.
- Design and Implementation:We translate security requirements into the AI application design and perform necessary implementations and modifications.
- Security Review: This reviewverifies that agreed-upon security requirements are appropriately reflected in the design and implementation.
* A re-evaluation of the improved AI application from an attacker's perspective to confirm the effectiveness of the countermeasures is offered as an option.
[Main areas of improvement and implementation]
The standard support covers the following AI-specific security areas. Necessary measures will be selected based on the configuration and challenges of the target system.
- LLM Prompt
We implement a multi-layered defense against prompt injection and system prompt leakage by combining input/output verification and a review of instruction structures.
- RAG
By implementing search controls and data separation based on user permissions, we reduce the risk of unauthorized information being disclosed through AI.
- AI Agent
By limiting the available tools and permissions to the bare minimum and incorporating human approval for critical operations, we reduce the risk of unintended actions by AI.
- MCP and external tool integration
By controlling the connection destination, verifying runtime arguments, managing authentication information, and recording execution history, we will build a system that prevents AI-generated instructions from being unconditionally passed to external systems.
- AI data
We will define the scope of what can be input, referenced, and output to the AI, including personal information and trade secrets, and implement features such as detection and masking of confidential information.
* We can also provide optional support for modifications to related areas such as web/API authentication/authorization and cloud-based access control, in addition to the above.
[Support methods tailored to the company's development structure]
- Implementation Advice:Your development team implements the solution, and our expert team provides support with improvement design, implementation advice, and reviews.
- Joint development:Implementation is carried out jointly by the customer's development team and a specialist team.
- Implementation outsourcing:A specialized team handles everything from formulating improvement plans to design and implementation.
Our company will handle customer inquiries and overall coordination, providing support in collaboration with specialized teams.
The specific implementation details and deliverables will be determined based on the client's development structure and contract scope.
■ Inquiries about the 'AI Security Improvement and Implementation Support Service'
株式会社サイバーセキュリティクラウド
戦略事業室
TEL:03-6416-9996
URL:https://www.cscloud.co.jp/ai-security-remediation/
■ Regarding the development of Cybersecurity Cloud's AI security business
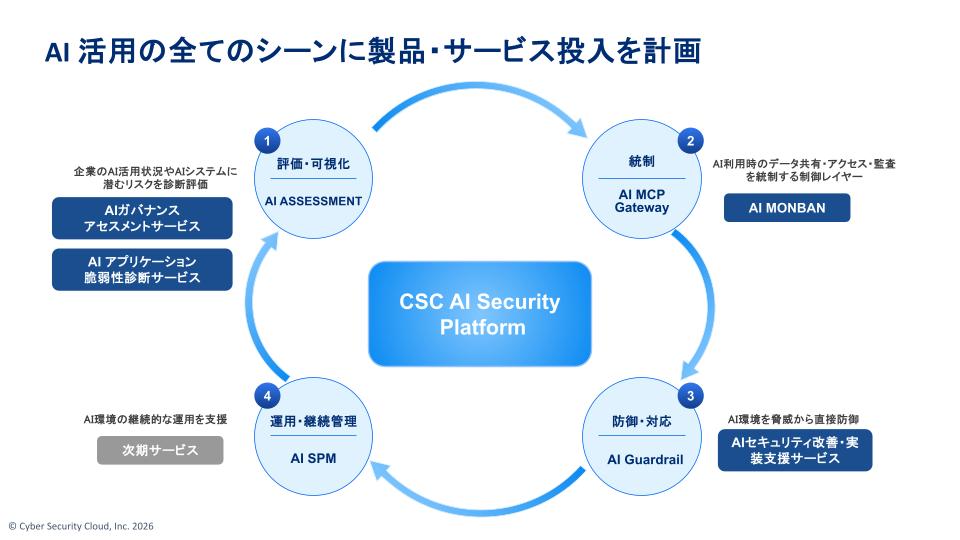
Our company has been actively expanding into the AI security field since 2026. Starting with the establishment of the "AI Trust Board," a specialized organization to promote AI governance, in April we launched "AI MONBAN" in June to control the use of AI, the "AI Application Vulnerability Assessment Service" in July to find AI-specific vulnerabilities, and the "AI Governance Assessment Service" in August to evaluate AI management systems.
By adding this new service that "fixes" the problems found, we will expand our service system to support companies' use of AI from all aspects: "control," "detect," "evaluate," and "fix."
|
service |
subject | role |
| AI MONBAN | AI utilization within companies and data flow between AI and internal systems |
|
| AI applications Vulnerability assessment service |
LLM, RAG, MCP, AI agents, etc. AI applications |
|
| AI governance Assessment Services |
Actual state and management system of AI use within companies |
|
| AI security improvement and implementation Support services |
LLM, RAG, MCP, AI agents, etc. AI applications |
|
AI is already gaining prominence as a crucial infrastructure that will influence corporate competitiveness. Our company will systematically introduce products and services that address all aspects of corporate AI utilization, and support corporate growth by providing an environment in which AI can be used safely and securely.
Cyber Security Cloud, Inc. (https://www.cscloud.co.jp)
Address: 13th Floor, JR Tokyu Meguro Building, 3-1-1 Kami-Osaki, Shinagawa-ku, Tokyo 141-0021, Japan
Representative: Toshihiro Koike Representative Director, President and CEO
Established: August 2010
With the mission of "creating a safe and secure cyberspace for people all over the world," we are a Japanese security manufacturer that provides web application security services utilizing world-leading cyber threat intelligence, as well as vulnerability information collection and management tools and fully managed security services for cloud environments. As one of the global companies in cybersecurity, we will contribute to solving social issues related to cybersecurity and providing added value to society.