
News
- Press Release
Share


Addressing concerns over a series of cyberattacks, we are offering 'AI Security Check 2026,' a free service to assess AI usage risks, to the first 10 companies to receive it.
With the momentum for security review on the rise, it's time to examine the new "areas that need protection": generative AI and AI agents.
Cyber Security Cloud, Inc. (Headquarters: Shinagawa-ku, Tokyo; Representative Director, President and CEO: Toshihiro Koike; hereinafter referred to as "the Company"), a global security manufacturer, will offer its "AI Security Check 2026" service, which allows experts to easily check the usage status and security challenges of generated AI and AI agents, to the first 10 companies that apply. This service is being offered free of charge to the first 10 companies that apply, in light of the increasing number of cyberattacks targeting domestic companies, the growing number of ransomware incidents and personal information leaks, and the expanding use of AI in companies.
In response to a series of corporate data breaches and cyberattacks, our company established an "Emergency Security Consultation Service" on October 6, 2026, to provide free initial consultations and investigations.
As security risks surrounding businesses diversify, the use of generative AI and AI agents in business operations is rapidly expanding. This has increased the need to understand and manage not only the traditional IT environment, but also the usage status, connection destinations, and data handled by AI. As part of our efforts to support companies in reviewing their security, we are now offering "AI Security Check 2026," which helps companies understand the actual state and risks of AI use in their operations and organize issues that should be prioritized for review and action.
■ Background of the provision of 'AI Security Check 2026'
In Japan, a series of incidents such as unauthorized access, data breaches, and ransomware attacks have highlighted the growing need for companies to review their security measures.
At the same time, as AI utilization advances, the scope of what companies must protect is also expanding. In addition to generative AI such as ChatGPT, AI use is evolving beyond simply inputting and generating information to deeply involve internal data and business processes. This includes RAG, which references internal data, AI agents that perform processing in conjunction with business systems, and MCP, which connects AI with external tools and data.
The Information-technology Promotion Agency, Japan (IPA) has published its "Top 10 Information Security Threats 2026," in which "cyber risks related to the use of AI" was selected for the third time as a threat to organizations. A variety of risks have been pointed out, including unintentional information leaks due to insufficient understanding of AI, and the ease and sophistication of cyberattacks due to the misuse of AI.
In this context, companies are required to understand not only their existing IT environment, but also who is using the AI they employ in their operations, how they are using it, what kind of information they are handling, and which systems and services they are connected to.
To address concerns such as "Is our company's use of AI safe?" and "Where should we start taking countermeasures?", we will help companies organize their current AI usage and identify priority issues through "AI Security Check 2026."
Source: IPA "Top 10 Information Security Threats 2026"
■What is 'AI Security Check 2026'?
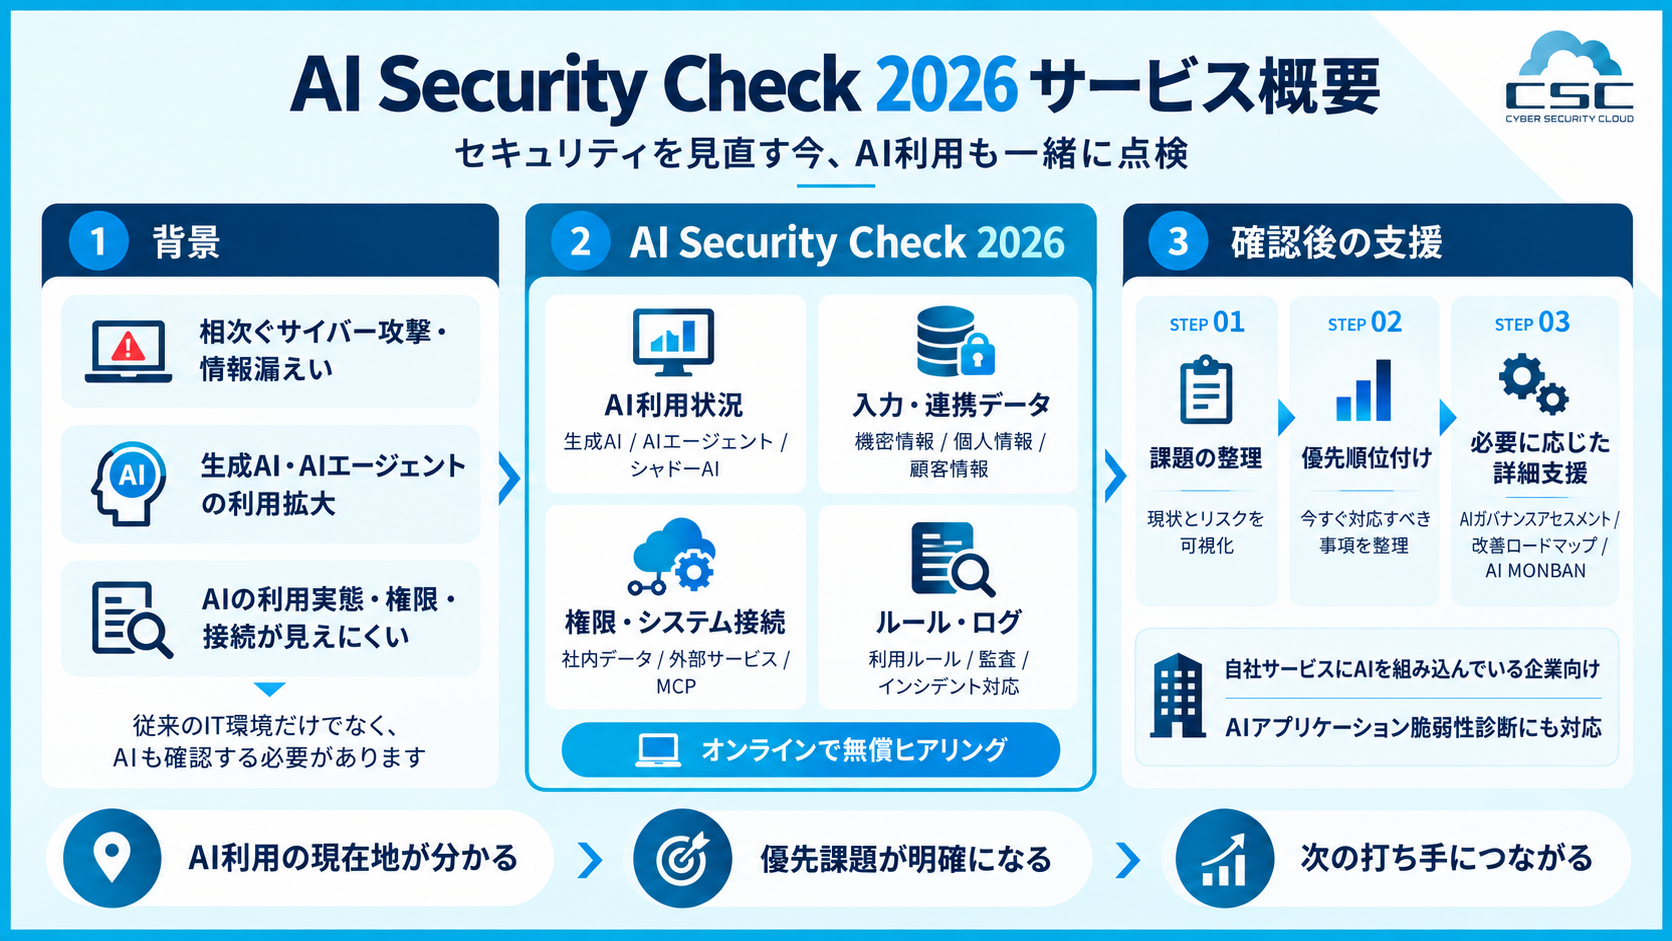
Through online interviews with experts, we will briefly review the current state of AI usage and security risks within companies, primarily from the following perspectives.
- Usage Status: Generative AI and AI agents used within the company, their users, and their purposes of use.
- Information handled: Confidential and personal information entered into and linked to the AI.
- Access Permissions: Internal data and systems that the AI can access, and the permissions it has been granted.
- Rule implementation: The gap between the status of AI usage rules and actual usage.
- External connectivity: Connection status with external tools and services via MCP, etc.
- Management and response system: System for acquiring and managing AI usage logs, auditing, and incident response.
We will identify who is using which AI, for what purpose, and what data and systems it is connected to, and then prioritize the areas that need improvement.
■Supporting the creation of an environment where AI can be used safely.
In promoting the use of AI, we believe it is crucial to understand its actual usage and associated risks, and to establish appropriate rules and technical management mechanisms for each.
If this check determines that more detailed verification and countermeasures are necessary, we will provide support for detailed evaluations using our "AI Governance Assessment Service" or technical controls using our AI governance platform "AI MONBAN," depending on the issue.
Furthermore, we also offer an "AI Application Vulnerability Assessment Service" to companies that have incorporated LLM, RAG, AI Agent, MCP, etc., into their own services or business systems.
Companies must protect the AI they use. Companies must protect the AI they create.
Our company will support security throughout the entire AI utilization lifecycle, from AI implementation and use to development and operation.
■“AI Security Check 2026” overview
| item | Content |
| subject | Companies that are using or considering implementing generation AI/AI agents in their business operations. |
| Content | A simple check of AI usage, the information handled, access permissions, usage rules, external connections, log management, and response system. |
| cost | Free |
| Implementation method | Online consultations with experts |
| Number of target companies | First 10 companies |
■ Application form for 'AI Security Check 2026'
Application form:https://lp.cscloud.co.jp/ai-governance-quick-assessment/inquiry/
Cyber Security Cloud, Inc. (https://www.cscloud.co.jp)
Address: 13th Floor, JR Tokyu Meguro Building, 3-1-1 Kami-Osaki, Shinagawa-ku, Tokyo 141-0021, Japan
Representative: Toshihiro Koike Representative Director, President and CEO
Established: August 2010
With the mission of "creating a safe and secure cyberspace for people all over the world," we are a Japanese security manufacturer that provides web application security services utilizing world-leading cyber threat intelligence, as well as vulnerability information collection and management tools and fully managed security services for cloud environments. As one of the global companies in cybersecurity, we will contribute to solving social issues related to cybersecurity and providing added value to society.